

Ransomware victim disclosure
← All victimsUnknown Education / Labor Union
Claimed by N0n · listed 5 hours ago
Status timeline
- ListedOct 6, 2026
Current state: Listed for ransom
At a glance
- Group
- N0n
- Status
- Listed for ransom
- Country
- United States
- Sector
- Education / Labor Union
- Listed on leak site
- Oct 6, 2026
- Records
- 181420
About the victim
AI dossier — public-source company profileA labor union based in New York representing members across education and nursing sectors, including teacher and nurse federations. The organization manages grievance, arbitration, and health-benefit operations for its membership.
- Industry
- Labor Union / Education
- Address
- New York, United States
Attack summary
Severity: critical — Exfiltration of 181,420+ documents containing personally identifiable information (member names in case files), sensitive employment records, health-benefit data, and confidential legal/arbitration materials affecting thousands of union members. This constitutes regulated PII and sensitive personnel data at scale.The N0n group claims to have encrypted the union's network and exfiltrated approximately 181,420 documents from the legal case archive, including grievance files, arbitration decisions, personnel records, collective bargaining agreements, and health-benefit materials. The group states it has destroyed backups and is threatening to publish data in batches.
Data the group says was taken
AI dossier — extracted from the leak post- Legal case archive (grievance and arbitration files)
- Disciplinary appeal decisions
- Personnel case files
- Collective bargaining agreements (CBAs)
- Memoranda of understanding (MOUs/MOAs)
- Nurse-federation case materials
- Health-benefit-fund records
- Teacher evaluation files
- Class-size complaint files
- Staff audit logs
What the group claims
US New York-based education or labor union organization
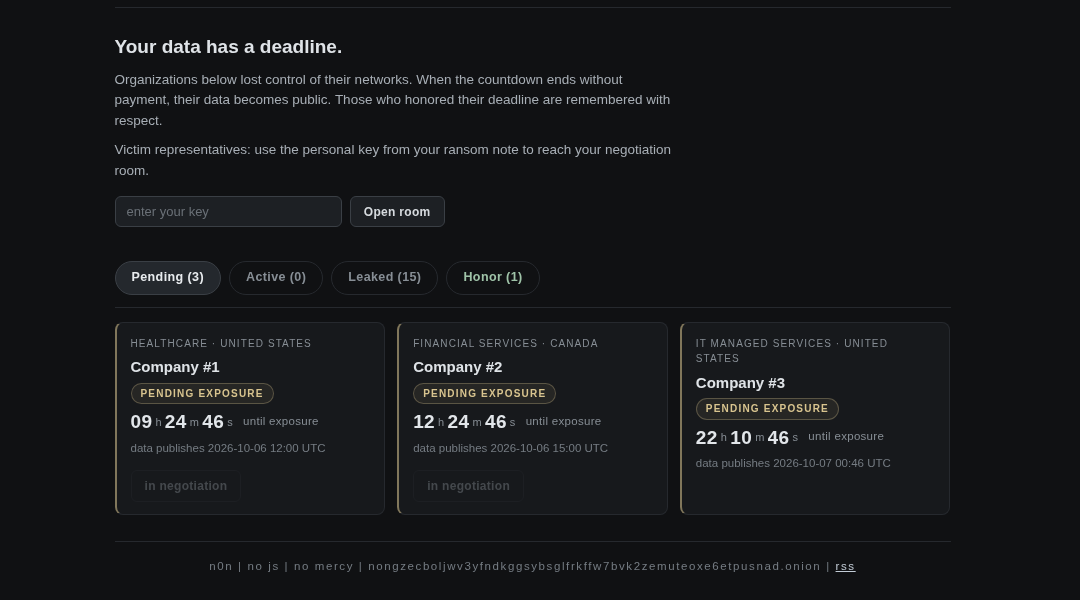
The leak post
captured from the group's site# Your data has a deadline. Organizations below lost control of their networks. When the countdown ends without payment, their data becomes public. Those who honored their deadline are remembered with respect. Victim representatives: use the personal key from your ransom note to reach your negotiation room. ### FinSoft (Kolibri retail back-office software) Retail software vendor / IT services · Uzbekistan #### What will be published if no settlement is reached * Everything: client databases of 10+ retail chains (keddo, marc, lancaster, comf_rus and others), the back-office platform and API service data Their business operations are fully stopped. Nothing restores operations without settlement — all backups and shadow copies are encrypted or destroyed. ### AFRICA-TECH (IT services / document processing) IT services / document services · Mali #### What will be published if no settlement is reached * Client documents: scans, attestations, insurance and embassy files, shared business folders Operations are fully stopped. Nothing restores without settlement — all backups and shadow copies are encrypted or destroyed. ### Fanatics (global sports commerce platform) Sports commerce …
Data the group says was taken
- legal case archive
- grievance and arbitration files
- disciplinary appeal decisions
- personnel case files
- contract documents
- CBAs
- MOUs
- MOAs
- side letters
- nurse-federation case materials
- health-benefit-fund case materials
- teacher evaluation files
- class-size complaint files
- staff audit logs
Screenshot of the leak post
Sources
Source
Indexed 5 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.