

Ransomware victim disclosure
← All victimsGress Clark Young & Schoepper
listed as Gress Clark Young & Schoepper (second listing) · Claimed by Rhysida · listed 4 hours ago
Status timeline
- ListedOct 13, 2026
Current state: Listed for ransom
At a glance
- Group
- Rhysida
- Status
- Listed for ransom
- Country
- United States
- Sector
- Legal
- Listed on leak site
- Oct 13, 2026
- Data size
- ~166.4 GB
- Records
- 167,804 files
About the victim
AI dossier — public-source company profileGress Clark Young & Schoepper is a US-based law firm operating a general practice. The firm maintains client trust accounts (IOLTA), handles personal injury and settlement cases, and processes workers' compensation matters through state administrative bodies.
- Industry
- Legal Services
Attack summary
Severity: critical — Confirmed exfiltration of regulated sensitive data at massive scale: HIPAA-protected medical records, SSNs and PII for clients/witnesses, IOLTA banking details, court credentials, and evidence of potential ethics violations. The data includes identifiable health information, financial account details, and materials enabling identity theft and check fraud. Cross-firm exposure (multiple law firms and Anne Arundel County government mentioned) compounds the scale.Rhysida claims to have exfiltrated approximately 166.4 GB of data from the firm's systems, including complete client databases, banking details, medical records, financial documents, and internal case files. The group is advertising the data for sale, claiming exclusive ownership will transfer to a single buyer.
Data the group says was taken
AI dossier — extracted from the leak post- Client trust account (IOLTA) details with wire-transfer information
- Personal identification documents (driver's licenses, birth certificates)
- Social Security numbers from W-9/W-2 forms
- Medical records and imaging (X-rays, HIPAA-protected health information)
- Settlement checks and check fraud-enabling artifacts
- Complete client database spanning multiple years
- Firm QuickBooks financial records and VOID checks
- Court e-filing system credentials (SPC e-file access)
- Case management files and expert-payment records
- Internal disciplinary records
- Doctor coaching letters indicating potential ethics violations
The group's post references roughly 167804 files advertised proof files.
What the group claims
Law firm (likely Pacific Northwest based on BIIA reference) with banking details for firm and clients, SSNs, signatures, W-9/I-9/W-4 forms, BIIA case-management data, QuickBooks company file, VOID checks, medical photos, PHI, coaching letters to doctors, court e-filing credentials, and disciplinary action against partner Daniel W. Gress.
The leak post
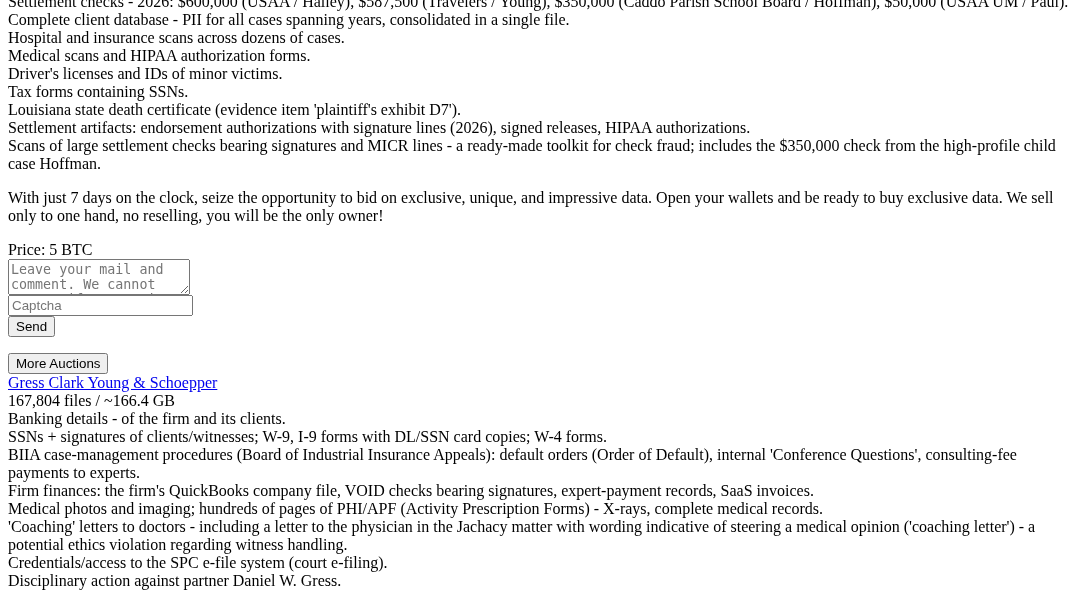
captured from the group's site94,604 files / ~51.3 GBACH instructions for the firm's client trust account (IOLTA) with complete account details; clients' wire-transfer details.PII: W-9/W-2 forms with SSNs, Massachusetts driver's licenses, birth certificate, personal UBS documents of a financial advisor.Client money flows (incoming/outgoing funds by case).Signed conflict-of-interest letter (matter - Alhassan) - a direct written admission of an internal firm problem. With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner! [Charles E. Tabor AAL LLC](https://www.charlestaborlaw.com) 96,456 files / ~114.5 GBSettlement checks - 2026: $600,000 (USAA / Hailey), $587,500 (Travelers / Young), $350,000 (Caddo Parish School Board / Hoffman), $50,000 (USAA UM / Paul).Complete client database - PII for all cases spanning years, consolidated in a single file.Hospital and insurance scans across dozens of cases.Medical scans and HIPAA authorization forms.Driver's licenses and IDs of minor victims.Tax forms containing SSNs.Louisiana state death certificate (evide…
Data the group says was taken
- banking details
- SSNs
- signatures
- W-9 forms
- I-9 forms
- W-4 forms
- QuickBooks files
- VOID checks
- medical photos
- PHI
- X-rays
- medical records
- court e-filing credentials
- disciplinary records
- coaching letters
Screenshot of the leak post
Sources
Source
Indexed 4 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.