

Ransomware victim disclosure

← All victims

Fanatics

Claimed by N0n · listed 1 hour ago

108 GB
Data size
46902 records
Today
Age
since listed · listed for ransom

Status timeline

  1. ListedSep 29, 2026

Current state: Listed for ransom

At a glance

Group
N0n
Status
Listed for ransom
Listed on leak site
Sep 29, 2026
Data size
108 GB
Records
46902

About the victim

AI dossier — public-source company profile

Fanatics is a global sports commerce platform operating in the United States. The company operates an online retail business serving sports fans and partners with leagues and brands.

Industry
Sports commerce / e-commerce

Attack summary

Severity: critical — Confirmed exfiltration of customer PII at scale (46,902 orders with personal data), financial transaction records, and tax documentation. Additionally, bank transaction archives and accounts-payable data represent sensitive business and customer financial information. The claimed destruction of backups indicates operational disruption.

The N0n group claims to have exfiltrated complete order history, accounts-payable invoices from league and brand partners, customer balances, bank transaction archives, and customer tax exemption certificates. The group states it has encrypted or destroyed backups and shadow copies, and claims deletion of cloud data has begun.

critical

Data the group says was taken

AI dossier — extracted from the leak post
  • Order history (46,902 order files)
  • Customer personal data
  • Accounts-payable invoices
  • Customer account balances
  • Bank transaction archive
  • Customer tax exemption certificates

What the group claims

Global sports commerce platform

The leak post

captured from the group's site
# Your data has a deadline.
Organizations below lost control of their networks. When the countdown ends without payment, their data becomes public. Those who honored their deadline are remembered with respect.
Victim representatives: use the personal key from your ransom note to reach your negotiation room.
### FinSoft (Kolibri retail back-office software)
Retail software vendor / IT services · Uzbekistan
#### What will be published if no settlement is reached
  * Everything: client databases of 10+ retail chains (keddo, marc, lancaster, comf_rus and others), the back-office platform and API service data


Their business operations are fully stopped. Nothing restores operations without settlement — all backups and shadow copies are encrypted or destroyed.
### AFRICA-TECH (IT services / document processing)
IT services / document services · Mali
#### What will be published if no settlement is reached
  * Client documents: scans, attestations, insurance and embassy files, shared business folders


Operations are fully stopped. Nothing restores without settlement — all backups and shadow copies are encrypted or destroyed.
### Fanatics (global sports commerce platform)
Sports commerce …

Data the group says was taken

  • order history files
  • customer personal data
  • accounts-payable invoices
  • customer balances
  • bank transaction archive
  • customer tax exemption certificates

Screenshot of the leak post
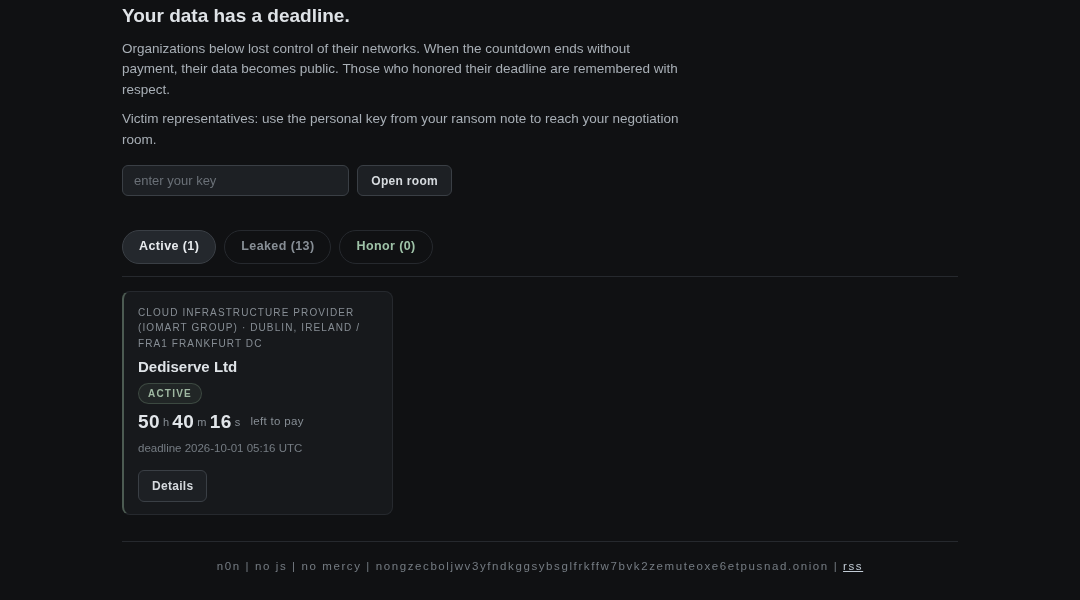
Leak screenshot for Fanatics

Sources

Source

Indexed 1 hour ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About N0n

N0n is a ransomware group first observed in September 2026 with an apparent financial motivation, having claimed at least 9 victims across a geographically diverse target set spanning Vietnam, the United States, Luxembourg, Brazil, and Argentina. Given the recency of their emergence and the limited volume of publicly documented activity, no verified attribution regarding country of origin, affiliation with known threat actors, or operational infrastructure has been established by CISA, the FBI, Mandiant, or other reputable security research organizations at this time. Their targeting pattern suggests an opportunistic rather than narrowly focused operational approach, with victims identified across the financial services, education, healthcare, government and defense, and general industry sectors, indicating a broad victim selection methodology rather than sector-specific specialization. No specific initial access vectors, malware tooling, encryption methods, or extortion tactics have been publicly attributed to this group in open-source intelligence reporting, and no major high-profile campaigns, record ransom demands, or law enforcement actions have been publicly documented against them. As of the time of this profile, N0n remains a nascent and poorly understood threat actor warranting continued monitoring given their cross-continental targeting scope and presence in sensitive sectors, though the low victim count and absence of corroborating technical reporting limit definitive characterization of their capabilities or long-term operational intent. The group has been linked to 23 public disclosures across our corpus. First observed on a leak site on September 18, 2026; most recent post September 29, 2026. The operation is currently active.

Timeline of this disclosure

  • September 29, 2026Fanatics listed by N0n on the group's public leak site
Data size
108 GB
Records
46902

Sector and geography

This disclosure adds to ransomware activity in the Sports commerce / e-commerce sector. Geographically, Fanatics is reported in United States, a country with 11,033 ransomware disclosures in our corpus.

If your organisation is affected

A listing by N0n means Fanatics appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CISA (United States), as required for your jurisdiction.
  • Monitor for the data appearing on N0n's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.