

Ransomware victim disclosure
← All victimsPharmaceutical manufacturer (unnamed)
Claimed by N0n · listed 1 hour ago
Status timeline
- ListedSep 29, 2026
Current state: Listed for ransom
At a glance
About the victim
AI dossier — public-source company profileAn unnamed pharmaceutical manufacturer operating three sites in Türkiye, subject to GxP (Good Manufacturing Practice) regulatory requirements. The company maintains internal network infrastructure including remote-access systems and camera surveillance.
- Industry
- Pharmaceutical Manufacturing (GxP)
Attack summary
Severity: critical — Confirmed exfiltration of complete internal network-security architecture and 1.35M connection records from critical business systems (M365, SAP, camera networks) across all three sites of a GxP-regulated pharmaceutical manufacturer. Operational shutdown of all sites asserted. Exposure of security configurations and access logs enables further attacks on healthcare supply chain.The N0n ransomware group claims to have encrypted the company's networks across all three sites and exfiltrated 940 MB of internal network-security configurations and connection records from M365, Intune, SAP Concur, UniFi, and internal applications. The group states all sites are under a total network blackout until settlement.
Data the group says was taken
AI dossier — extracted from the leak post- Network-security configurations (all 3 sites)
- M365/Intune connection records (1.35M)
- SAP Concur transaction data
- UniFi camera system mappings
- Internal application access logs
- Remote-access configurations
What the group claims
Unnamed pharmaceutical manufacturing company operating 3 sites in Türkiye
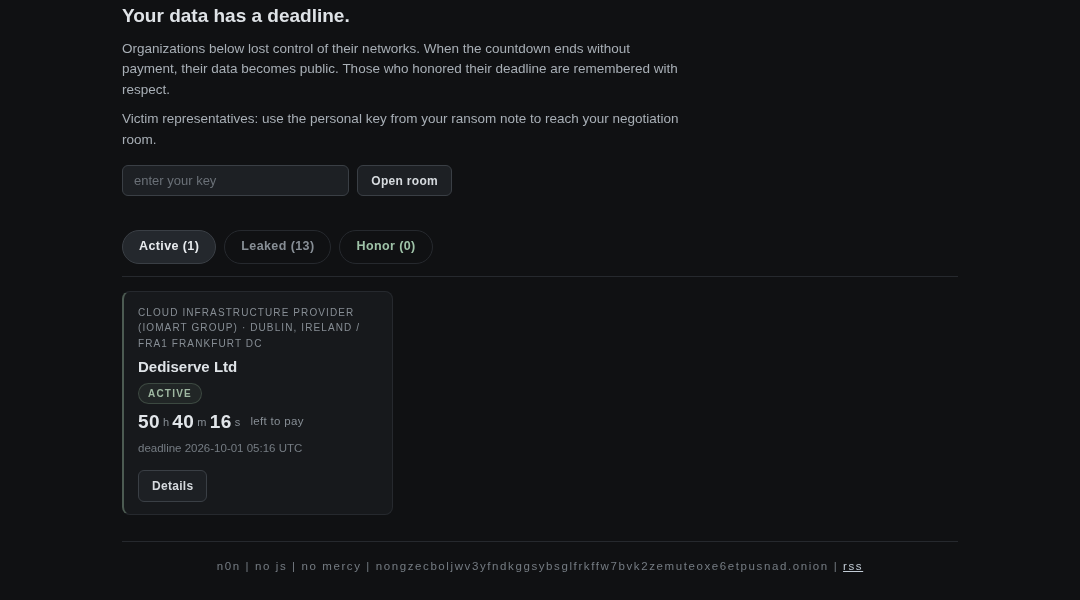
The leak post
captured from the group's site# Your data has a deadline. Organizations below lost control of their networks. When the countdown ends without payment, their data becomes public. Those who honored their deadline are remembered with respect. Victim representatives: use the personal key from your ransom note to reach your negotiation room. ### FinSoft (Kolibri retail back-office software) Retail software vendor / IT services · Uzbekistan #### What will be published if no settlement is reached * Everything: client databases of 10+ retail chains (keddo, marc, lancaster, comf_rus and others), the back-office platform and API service data Their business operations are fully stopped. Nothing restores operations without settlement — all backups and shadow copies are encrypted or destroyed. ### AFRICA-TECH (IT services / document processing) IT services / document services · Mali #### What will be published if no settlement is reached * Client documents: scans, attestations, insurance and embassy files, shared business folders Operations are fully stopped. Nothing restores without settlement — all backups and shadow copies are encrypted or destroyed. ### Fanatics (global sports commerce platform) Sports commerce …
Data the group says was taken
- network-security configuration
- device definitions
- remote-access mappings
- M365/Intune connection records
- SAP Concur records
- UniFi camera estate records
- internal application records
Screenshot of the leak post
Sources
Source
Indexed 1 hour agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.