

Ransomware victim disclosure
← All victimsArgentem Creek Partners
Claimed by N0n · listed 1 hour ago
Status timeline
- ListedSep 29, 2026
Current state: Listed for ransom
At a glance
- Group
- N0n
- Status
- Listed for ransom
- Country
- United States
- Listed on leak site
- Sep 29, 2026
- Data size
- 108 GB
- Records
- 2500000+
About the victim
AI dossier — public-source company profileArgentem Creek Partners is a United States-based investment management firm specializing in private credit. The company operates a corporate network infrastructure supporting investment operations and maintains an investor document delivery platform.
- Industry
- Investment management / private credit
Attack summary
Severity: critical — Confirmed exfiltration of internal network architecture, systems administration data, and tax/investor financial documents from a private credit firm. Scale and sensitivity of internal systems data combined with financial document exposure justifies critical rating.The N0n group claims to have encrypted Argentem Creek Partners' network and exfiltrated internal systems data and tax documents. The group states it has obtained 2.5M+ connection records mapping the firm's complete internal systems architecture, Active Directory, SharePoint, and office-security integrations, plus tax-season document flows from the firm and its investor document delivery platform.
Data the group says was taken
AI dossier — extracted from the leak post- Connection records (2.5M+)
- Active Directory configuration
- SharePoint data
- Internal systems map
- MSP tooling access logs
- Office-security integration records
- Tax-season document flows
- Investor document delivery platform data
What the group claims
Investment firm specializing in private credit
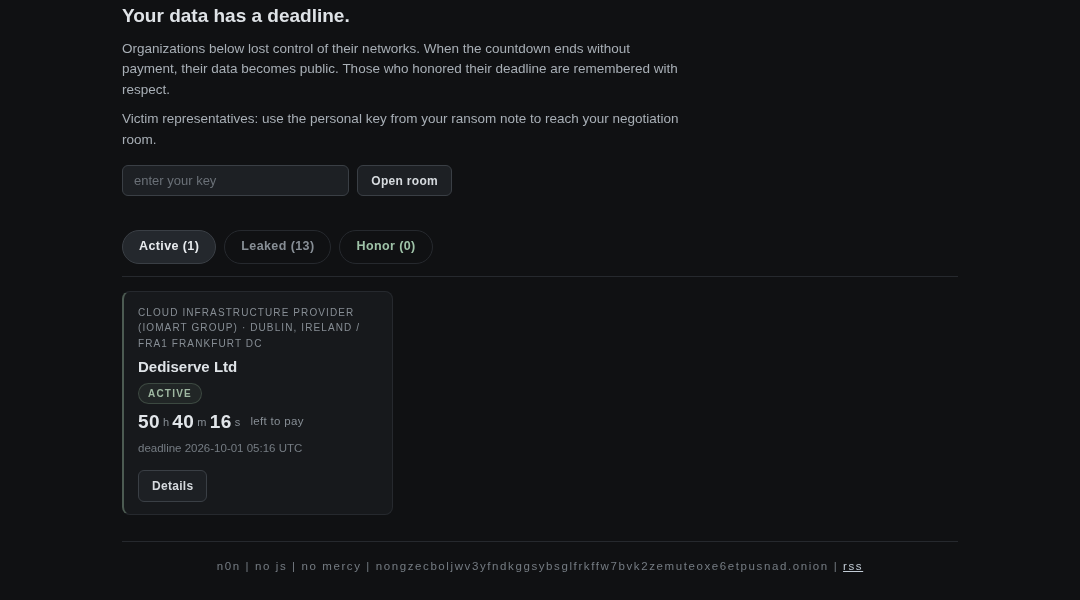
The leak post
captured from the group's site# Your data has a deadline. Organizations below lost control of their networks. When the countdown ends without payment, their data becomes public. Those who honored their deadline are remembered with respect. Victim representatives: use the personal key from your ransom note to reach your negotiation room. ### FinSoft (Kolibri retail back-office software) Retail software vendor / IT services · Uzbekistan #### What will be published if no settlement is reached * Everything: client databases of 10+ retail chains (keddo, marc, lancaster, comf_rus and others), the back-office platform and API service data Their business operations are fully stopped. Nothing restores operations without settlement — all backups and shadow copies are encrypted or destroyed. ### AFRICA-TECH (IT services / document processing) IT services / document services · Mali #### What will be published if no settlement is reached * Client documents: scans, attestations, insurance and embassy files, shared business folders Operations are fully stopped. Nothing restores without settlement — all backups and shadow copies are encrypted or destroyed. ### Fanatics (global sports commerce platform) Sports commerce …
Data the group says was taken
- corporate network data
- Active Directory data
- SharePoint data
- MSP tooling data
- office-security integrations
- tax-season document flows
- investor document delivery platform data
Screenshot of the leak post
Sources
Source
Indexed 1 hour agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.