

Ransomware victim disclosure

← All victims

Italy (Government/Data Protection)

Claimed by IAMNOTAVILLAIN · listed 44 minutes ago

150GB
Data size
85000+ records
Today
Age
since listed · listed for ransom

Status timeline

  1. ListedSep 30, 2026

Current state: Listed for ransom

At a glance

Status
Listed for ransom
Country
Italy
Listed on leak site
Sep 30, 2026
Data size
150GB
Records
85000+

About the victim

AI dossier — public-source company profile

The victim name references Italy (Government/Data Protection), suggesting Italian government entities and data protection infrastructure. The post claims exposure of 85,000+ files totalling 150GB across top departments, units, and offices.

Attack summary

Severity: critical — Alleged exfiltration of government data at scale (150GB, 85,000+ files) combined with confirmed personal and financial data from Revolut (KYC documents, bank accounts, crypto transactions, ID scans). Involves regulated financial services data and government records, meeting critical threshold.

IAMNOTAVILLAIN claims exfiltration of Italian government data and user records from Revolut (a fintech company). The group alleges Revolut ignored a data protection report and transferred customer KYC documents and transaction records across jurisdictions without proper authorization.

critical

Data the group says was taken

AI dossier — extracted from the leak post
  • KYC documents
  • Personal names
  • Email addresses
  • Phone numbers
  • Physical addresses
  • Bank account information
  • ID scans
  • Fiat transaction records
  • Cryptocurrency transaction records
  • Government department files

What the group claims

Italy is being exposed for failing to follow proper data protection laws. Includes 85,000+ files totaling 150GB. Top departments, units, and offices affected.

The leak post

captured from the group's site
Italy is being exposed for failing to follow proper data protection laws. 
Includes Includes 85,000+ Files — 150GB. Top departments, units, offices affected. 
Revolut data on sale. Contact information at the bottom of the page. 
### Buy exclusion of your data
You can pay to have your information removed before it is sold. Once excluded, your records will not be included in any future sale or distribution. 
This also applies to the . Limited option available until the sale is final. After that, no removals are possible. 
Contact: or use the Session button below. 
Revolut got a report about a user database. They ignored it, so we are exposing them for failing to keep user information secure, and for sending data from a different jurisdiction. 
We have everything, including KYC documents, address, phone number, email, bank accounts, and fiat and crypto transactions. 
An impersonator and scammer who used to work with us took a small sample we handed him and is now claiming the breach as his. That cut is not the full set. Revolut and the other companies sent the data to us. He did not do this. We can prove it: the originals, the volume, the conversations, and the companies that sent it.…

Data the group says was taken

  • government files
  • departmental records

Screenshot of the leak post
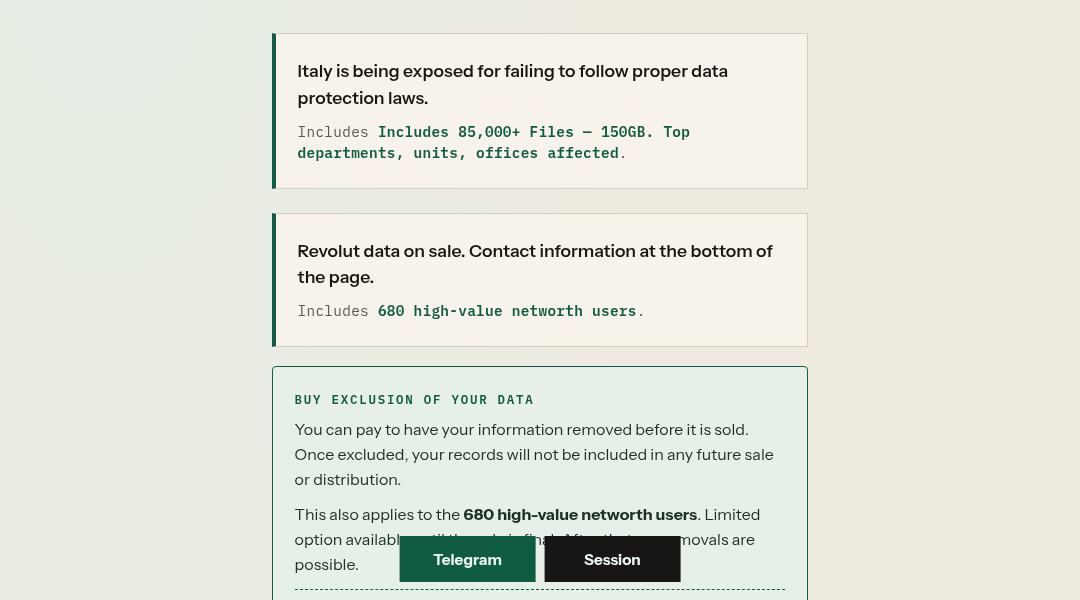
Leak screenshot for Italy (Government/Data Protection)

Sources

Source

Indexed 44 minutes ago

This page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.

Is this your supplier? Your competitor? You?

Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.

Disclosure context

About IAMNOTAVILLAIN

IAMNOTAVILLAIN is a ransomware group first observed in September 2026 with an apparent financial motivation, though limited public documentation exists given the group's nascent emergence and very low victim count. With only two known victims identified to date, both concentrated in Italy and spanning the financial services and government sectors, the group remains largely uncharacterized by major threat intelligence organizations including CISA, FBI, and Mandiant at this time. Due to the extremely limited operational history and absence of confirmed public reporting from authoritative sources, definitive attribution regarding country of origin, RaaS affiliation, specific tooling, initial access vectors, or extortion methodology cannot be responsibly assessed. The targeting pattern — specifically Italian financial and government entities — may suggest opportunistic selection or a deliberate regional focus, though the small sample size of two victims is insufficient to establish a reliable pattern. Given the group's very recent first observation date and minimal footprint, IAMNOTAVILLAIN should be considered an emerging and uncharacterized threat actor whose profile warrants continued monitoring as additional intelligence becomes available through credible reporting channels. The group has been linked to 3 public disclosures across our corpus. First observed on a leak site on September 29, 2026; most recent post September 30, 2026. The operation is currently active.

Timeline of this disclosure

  • September 30, 2026Italy (Government/Data Protection) listed by IAMNOTAVILLAIN on the group's public leak site
Data size
150GB
Records
85000+

Other recent disclosures by IAMNOTAVILLAIN

IAMNOTAVILLAIN has been linked to 3 public victims on Darkfield. A sample of the most recent:

See the full IAMNOTAVILLAIN dossier →

Sector and geography

This disclosure adds to ransomware activity in the Government sector, which has 685 disclosures indexed across all operators we track. Geographically, Italy (Government/Data Protection) is reported in Italy, a country with 635 ransomware disclosures in our corpus.

If your organisation is affected

A listing by IAMNOTAVILLAIN means Italy (Government/Data Protection) appeared on a ransomware extortion site and is being pressured to pay before any publication. If this is your organisation, or a supplier you depend on, the priority is to confirm the intrusion and contain it before the window to act closes.

  • Engage your incident-response team and preserve forensic evidence before remediating — do not wipe affected systems first.
  • Force a password reset and revoke active sessions for exposed accounts; rotate any credentials, API keys or certificates that may have been in the stolen data.
  • Assess regulatory notification duties (GDPR, NIS2, sector regulators) — many carry a 72-hour reporting clock from awareness.
  • Report the incident to your national CERT, CSIRT Italia (Italy), as required for your jurisdiction.
  • Monitor for the data appearing on IAMNOTAVILLAIN's leak site and across paste and breach channels, and brief downstream partners who may be exposed through you.

How we know this. Darkfield monitors public ransomware leak sites continuously, archiving every new disclosure and the data later released against the victim. Each entry on this page is sourced from the operator's own publication and cross-checked against complementary OSINT feeds (RansomLook, ransomware.live, RansomWatch). We do not collect or host stolen data — only the metadata, timestamps and screenshots needed to make the public disclosure searchable and accountable. Records here are corrected when the original post is edited, retracted, or merged with another disclosure.