

Ransomware victim disclosure
← All victimsUnknown Law Firm (Criminal Defense Practice)
Claimed by Rhysida · listed 2 hours ago
Status timeline
- ListedSep 27, 2026
Current state: Listed for ransom
At a glance
- Group
- Rhysida
- Status
- Listed for ransom
- Country
- United States
- Sector
- Legal
- Listed on leak site
- Sep 27, 2026
- Data size
- 710.6 GB / 338,542 files
- Records
- 338542 files
About the victim
AI dossier — public-source company profileA U.S.-based criminal defense law firm specializing in felony cases including DUI, domestic violence, fraud, and sex crimes. The practice maintains a caseload of approximately 175+ clients with documented cases involving federal immigration custody, probation violations, and risk protection orders.
- Industry
- Criminal Defense Law
Attack summary
Severity: critical — Exfiltration of comprehensive criminal case files for 175+ clients containing extensive PII (names, contact data, biometrics via FD-258 cards), victim and witness identity and location data protected under Marsy's Law, federal ICE custody records, GPS monitoring coordinates, and 206 GB of sensitive law enforcement video and audio. This represents mass exposure of vulnerable individuals in criminal proceedings and breach of attorney-client privilege.Rhysida claims to have exfiltrated a complete case dossier covering ~175+ criminal defense clients, including 206 GB of police bodycam video, 911 recordings, jail calls, incident reports, and victim/witness data. The group offers the data for auction with a 7-day deadline, claiming exclusive single-buyer sale.
Data the group says was taken
AI dossier — extracted from the leak post- Criminal case files (~175+ clients)
- Police bodycam video (206 GB)
- 911 recordings
- Jail call recordings
- Incident reports and photo lineups
- FCIC/NCIC forms
- Victim and witness personal data
- Client names and case details (felonies: sex sting, domestic violence, DUI, fraud)
- Attorney fee records ($750–$25,000)
- FDLE expungement packets with FD-258 fingerprint cards
- Risk Protection Order data
- ICE custody client records
- GPS monitoring data (material witness, 3+ years)
What the group claims
An unidentified law firm with a criminal defense practice. Data includes client dossiers covering ~175+ clients with felony, DUI, probation violation, and ICE custody matters, ~206 GB of bodycam video, 911 recordings, jail calls, police discovery files, FDLE expungement packets with fingerprint cards, victim and witness data, and attorney fee records ranging from $750 to $25,000. Also includes HR records with SSNs, bank account details, IOLTA trust account statements, and ACH/EFT authorizations.
The leak post
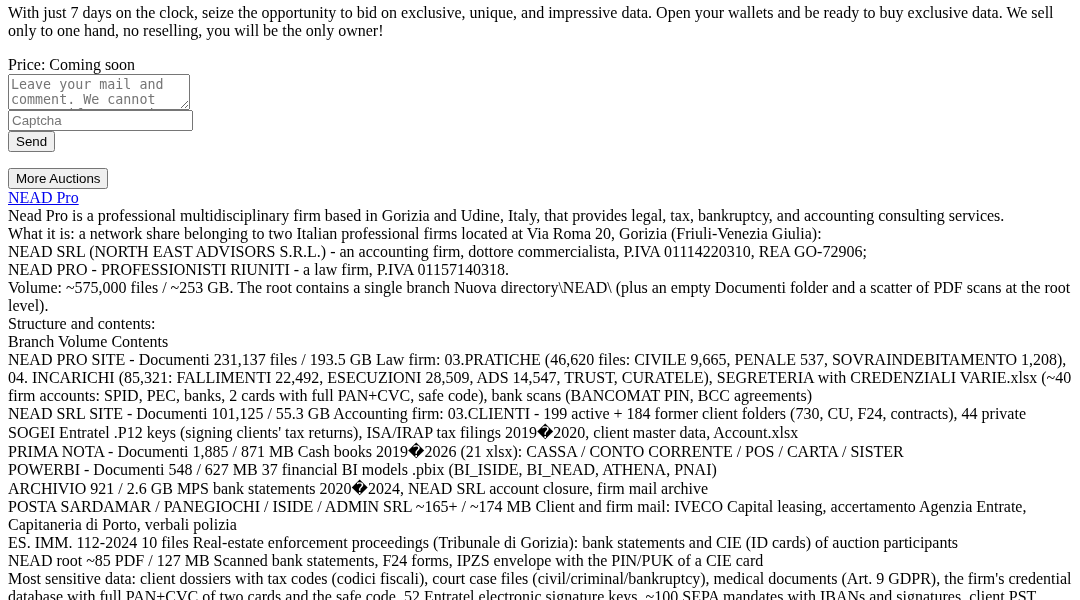
captured from the group's siteContents. A complete dossier of the firm's criminal defense practice covering ~175+ clients: felonies (an undercover sex sting involving a minor - Ramirez; domestic violence robbery - Valderrama, involving a 4-year-old child; felony DUI - Segula; fraud - B. Williams), a core caseload of ~10 DUI matters (including an arrest at breath readings of 0.011 and SCRAM alcohol monitoring), violations of probation (VOP), FDLE expungement packets with FD-258 fingerprint cards, a 'red flag' Risk Protection Order (RPO), 2 clients in ICE custody, and a material witness under GPS monitoring for 3+ years. Attorney fees range from $750 to $25,000. The case files include complete police discovery: ~206 GB of bodycam video, 911 recordings, and jail calls, incident reports, photo line-ups, FCIC/NCIC forms, and victim and witness data (Marsy's Law). With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner! Nead Pro is a professional multidisciplinary firm based in Gorizia and Udine, Italy, that provides legal, tax, bankruptcy, and account…
Data the group says was taken
- client case files
- bodycam video
- 911 recordings
- jail calls
- police discovery
- fingerprint cards
- victim and witness data
- bank account details
- IOLTA statements
- ACH/EFT authorizations
- HR records
- SSNs
- credit card statements
- W-9 forms
- check copies
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.