Ransomware victim disclosure
← All victimsNEAD SRL / NEAD PRO - Professionisti Riuniti
listed as Nead Pro / NEAD SRL · Claimed by Rhysida · listed 15 days ago
Status timeline
- ListedSep 29, 2026
Current state: Listed for ransom
At a glance
About the victim
AI dossier — public-source company profileNEAD SRL (NORTH EAST ADVISORS S.R.L.) is an accounting firm (dottore commercialista) and NEAD PRO is a law firm (professionisti riuniti), both based in Gorizia and Udine, Italy. Together they form a multidisciplinary professional practice providing legal, tax, bankruptcy, and accounting consulting services to Italian and international clients.
- Industry
- Legal, Tax, Bankruptcy & Accounting Consulting
- Address
- Via Roma 20, Gorizia (Friuli-Venezia Giulia), Italy
Attack summary
Severity: critical — Confirmed exfiltration of large-scale regulated and highly sensitive data: US taxpayer SSNs and banking credentials, Italian tax codes, criminal case files with minor victims and undercover operations, medical documents, electronic signature keys, full payment card data, and extensive personal identifying information on hundreds of individuals across multiple jurisdictions. Material witness and ICE custody information exposed. Data is actively being auctioned.Rhysida claims to have exfiltrated approximately 253 GB (~575,000 files) from shared network storage belonging to both firms. The breach includes law firm case files (civil, criminal, bankruptcy), accounting client records, tax filing materials, banking credentials, electronic signature keys, and sensitive personal and medical documents. The group is actively auctioning the data with a 7-day deadline.
Data the group says was taken
AI dossier — extracted from the leak post- Law firm case files (civil, criminal, bankruptcy, debt restructuring)
- Criminal defense case dossiers (~175+ clients with felony/DUI/fraud matters)
- Police discovery materials (~206 GB bodycam video, 911 recordings, jail calls)
- Tax filings and returns (730, CU, F24 forms)
- Client tax codes (codici fiscali)
- IRS W-9 forms and 1099 transmissions (US HOA/vendor data)
- Social Security numbers and bank account numbers (US homeowners)
- ACH debit files with routing/account numbers
- Brokerage statements (USAA)
- Bank signature cards and credentials
- SEPA mandates with IBANs and signatures
- Electronic signature keys (44 private SOGEI Entratel .P12 keys)
- Firm credential database (full PAN+CVC of payment cards, safe code)
- Medical documents
- HUD-1 home purchase settlements
- Bankruptcy assessments and hardship letters
- Passports of foreign shareholders
- SQL Server databases (RM_Warehouse, RM_Sales, RM_Portals, CiraNet, CiraBooks)
- Financial BI models (.pbix files)
- Bank statements (MPS 2020–2024)
- Client PST archives (7.5 GB email)
- Real-estate enforcement documents and auction participant ID cards
What the group claims
A professional multidisciplinary firm based in Gorizia and Udine, Italy, providing legal, tax, bankruptcy, and accounting consulting. Includes NEAD SRL (accounting, P.IVA 01114220310) and NEAD PRO - PROFESSIONISTI RIUNITI (law firm, P.IVA 01157140318). Data includes client dossiers, court case files, tax filings, credential database with full PAN+CVC, Entratel signing keys, SEPA mandates, and client phone backups.
The leak post
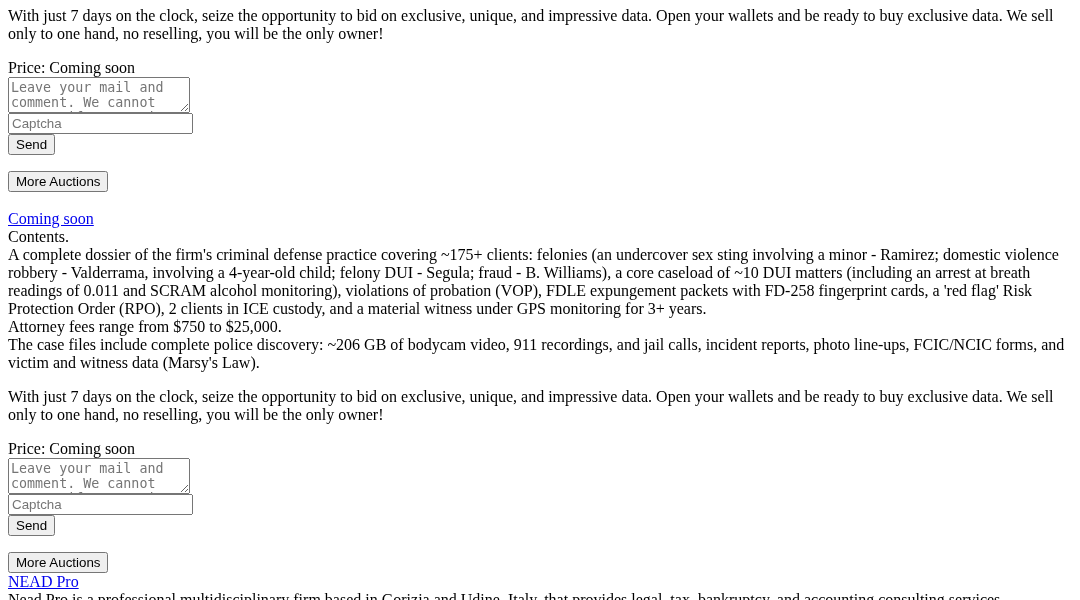
captured from the group's site2.478.837 files1.84 TBThe tax, banking and debt secrets of hundreds of American HOAs and thousands of homeowners - complete with SSNs, account numbers and signatures.Genuine W-9 forms with Social Security numbers, addresses and signatures; IRS 1099-MISC/NEC e-file transmissions for 2014�2025 - thousands of vendor TINs/SSNsHomeowners' banking keys: ACH debit files with routing and account numbers, USAA brokerage statements, signed bank signature cardsPeople's debts by name: assessments through September 2026, bankruptcies, late-fee waivers, hardship letters from debtors begging for payment plansPersonal documents: HUD-1 home purchase settlements (names, prices, mortgages), signed waivers with addresses, HOA election ballots with voter namesFull SQL Server databases: RM_Warehouse, RM_Sales, RM_Portals, CiraNetIdentity (portal accounts), CiraBooks_GL (general ledger)Mail and document flow: CiraMail$, CiraDocs$, SalesDocs$ With just 7 days on the clock, seize the opportunity to bid on exclusive, unique, and impressive data. Open your wallets and be ready to buy exclusive data. We sell only to one hand, no reselling, you will be the only owner! Contents. A complete dossier of the firm's…
Data the group says was taken
- client dossiers
- court case files
- tax filings
- codici fiscali
- medical documents
- credential database
- PAN+CVC card data
- safe code
- Entratel electronic signature keys
- SEPA mandates with IBANs
- bank statements
- passport copies
- PST archives
- phone backup
- financial BI models
- cash books
Screenshot of the leak post
Sources
Source
Indexed 15 days agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.