

Ransomware victim disclosure
← All victimsSCA Logistik & Fulfillment GmbH
Claimed by AUR0RA · listed 3 hours ago
Status timeline
- ListedSep 17, 2026
- Data leakeddate unknown
At a glance
- Group
- AUR0RA
- Status
- Data leaked
- Country
- Germany
- Sector
- Logistics & Fulfillment
- Listed on leak site
- Sep 17, 2026
- Data size
- 5.7 GB
- Records
- 124000 files
About the victim
AI dossier — public-source company profileSCA is a Bavarian logistics and e-commerce fulfillment provider offering order processing, shipment, returns management, and warehouse automation services to customers across Europe.
- Industry
- Logistics & E-commerce Fulfillment
Attack summary
Severity: high — Confirmed exfiltration of employee personal data, tax/banking records, and business-critical information (customer orders, contracts, source code). Combined scope and sensitivity of workforce PII, financial records, and operational IP constitutes significant business impact.AUR0RA claims to have exfiltrated 5.7 GB of data including customer orders, shipments, returns, employee and applicant files, management records, tax and banking documentation, warehouse automation systems, source code, and customer contracts.
Data the group says was taken
AI dossier — extracted from the leak post- customer orders and shipments
- employee and applicant personal files
- tax and banking records
- management records
- warehouse automation source code
- customer contracts
What the group claims
Bavarian logistics and e-commerce fulfillment provider.
The leak post
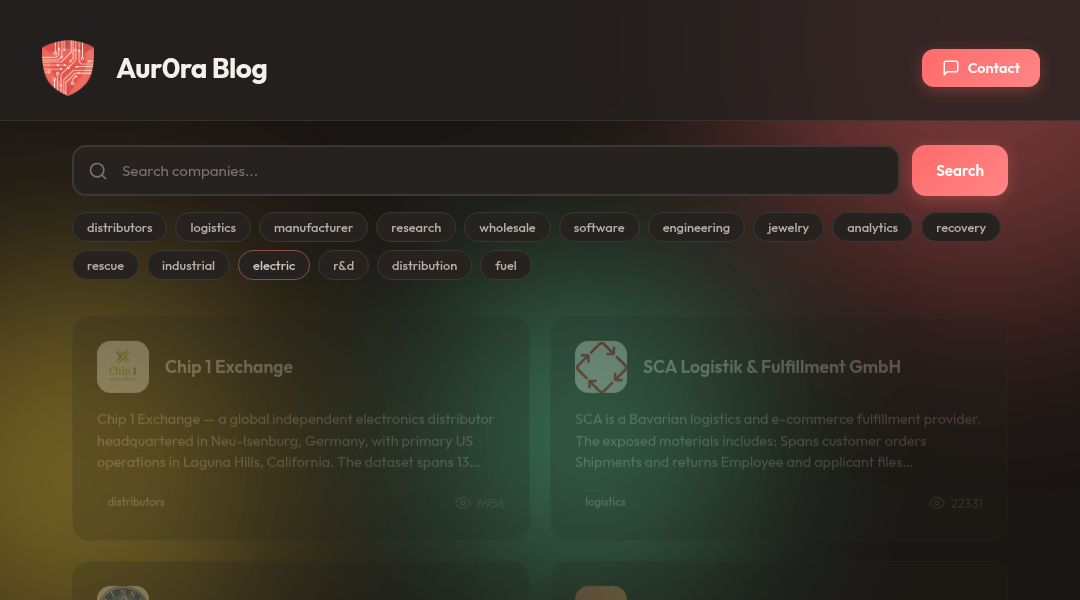
captured from the group's site[ Chip 1 Exchange — a global independent electronics distributor headquartered in Neu-Isenburg, Germany, with primary US operations in Laguna Hills, California. The dataset spans 13 years (2013-2026) of corporate operations and encompasses: 40+ passport photographs, I-9 forms with SSNs, W-4 tax forms, payroll registers — the complete identity theft toolkit for the entire US, Mexican, and European workforce. A Firefox saved-password vault (53 credentials) with its decryption key — granting immediate access to Wells Fargo corporate banking, NetSuite ERP, GoDaddy domain management, and 15+ supplier portals including Arrow, Farnell, Microchip, and Texas Instruments. Complete 2026 financial intelligence — P&L through July, executive financial health assessment, AR/AP aging, chart of accounts revealing all bank account numbers. 15+ exclusive franchise manufacturer agreements with pricing terms, territory allocations, and per-customer gross profit margins — the core competitive IP of a $100M+ distributor. ITAR registration and defense customer sales orders to Jabil Defense, Curtis-Wright, GEN3 Defense, and Cobham Remec — potential export control violation. 5.7 GB of Outlook PST email arch…
Data the group says was taken
- customer orders
- shipments and returns records
- employee and applicant files
- management records
- tax records
- banking records
- warehouse automation source code
- customer contracts
Screenshot of the leak post
Sources
Source
Indexed 3 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.