

Ransomware victim disclosure
← All victimsVan Eijck International Car Rescue B.V.
Claimed by AUR0RA · listed 3 hours ago
Status timeline
- ListedSep 17, 2026
- Data leakeddate unknown
At a glance
- Group
- AUR0RA
- Status
- Data leaked
- Country
- Netherlands
- Listed on leak site
- Sep 17, 2026
- Data size
- 168 GB+
- Records
- 500+ claims, 227 employee home directories, 18 user accounts, 206 groups
About the victim
AI dossier — public-source company profileVan Eijck International Car Rescue B.V. is a family-owned Dutch towing and recovery company operating 225+ vehicles across 20 branch offices in the Netherlands and Spain, with a workforce of 180+ employees providing roadside assistance and vehicle recovery services.
- Industry
- Towing & Vehicle Recovery Services
- Address
- Langendijk 5, 5652 AX Eindhoven, The Netherlands
- Employees
- 180+
Attack summary
Severity: critical — Confirmed exfiltration of regulated/sensitive data at scale: employee PII including tax records and salary information, customer identity documents and driving licenses, 10 years of claims data with personal information, complete identity infrastructure credentials, and financial database access. Compromises both operational security and data protection compliance obligations.AUR0RA claims to have exfiltrated 168 GB+ of data including identity infrastructure credentials (Azure AD Connect service account), 9 KeePass password vaults, firewall configurations for all 20 branches, employee personal and financial records, customer rental contracts with identity documents, 10 years of claims data with customer PII, complete Google Workspace backup, and Unit4 ERP database admin credentials.
Data the group says was taken
AI dossier — extracted from the leak post- Azure AD Connect service account credentials
- KeePass password vaults (9 total)
- FortiGate firewall configurations and credentials
- Employee home directories (227, 156 GB) with tax forms and salary records
- Customer rental contracts with identity documents and driving licenses
- 10 years customer claims data (500+ claims) with insurance details
- Google Workspace backup (Gmail, Drive, Calendar)
- Unit4 ERP financial databases
- Vehicle registrations
What the group claims
Family-owned Dutch towing and recovery company with 225+ vehicles, 180+ employees, and 20 branch offices across the Netherlands and Spain. Exposed data includes Azure AD Connect service account password, KeePass vaults, FortiGate firewall configurations, employee home directories, RentRunner customer rental contracts, customer claims data, Google Workspace backup, and Unit4 ERP admin credentials.
The leak post
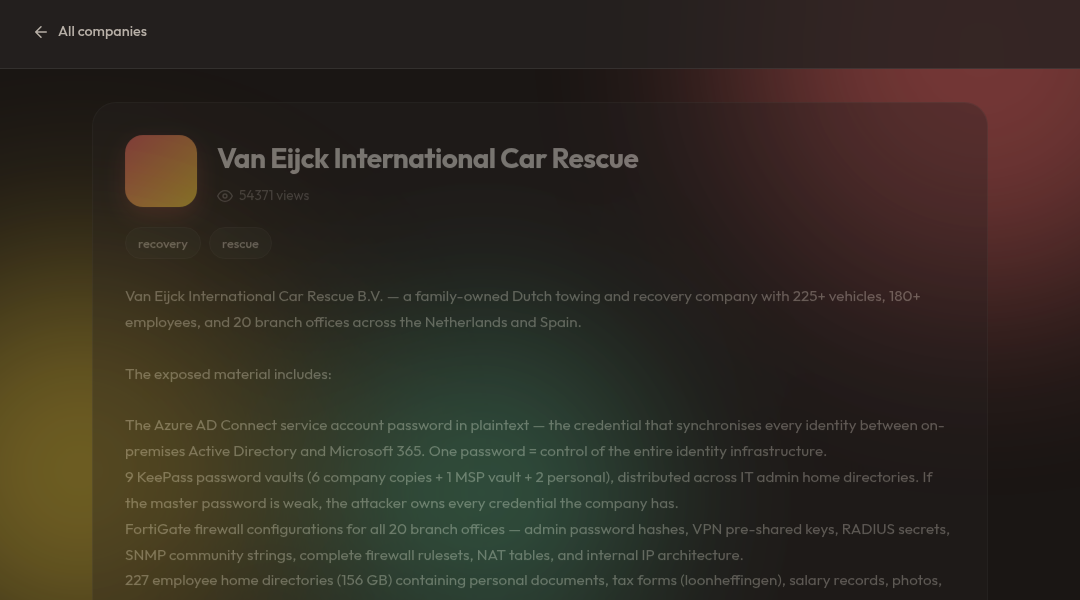
captured from the group's site# Van Eijck International Car Rescue Van Eijck International Car Rescue B.V. — a family-owned Dutch towing and recovery company with 225+ vehicles, 180+ employees, and 20 branch offices across the Netherlands and Spain. The exposed material includes: The Azure AD Connect service account password in plaintext — the credential that synchronises every identity between on-premises Active Directory and Microsoft 365. One password = control of the entire identity infrastructure. 9 KeePass password vaults (6 company copies + 1 MSP vault + 2 personal), distributed across IT admin home directories. If the master password is weak, the attacker owns every credential the company has. FortiGate firewall configurations for all 20 branch offices — admin password hashes, VPN pre-shared keys, RADIUS secrets, SNMP community strings, complete firewall rulesets, NAT tables, and internal IP architecture. 227 employee home directories (156 GB) containing personal documents, tax forms (loonheffingen), salary records, photos, and financial data. 12 GB of RentRunner customer rental contracts with copies of identity documents, driving licenses, and vehicle registrations. 10 years of customer claims data (20…
Data the group says was taken
- credentials
- firewall configurations
- employee personal documents
- tax records
- salary records
- customer contracts
- identity documents
- driving licenses
- vehicle registrations
- insurance details
- customer PII
- email backups
- financial databases
- ERP credentials
- password vaults
Screenshot of the leak post
Sources
Source
Indexed 3 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.