

Ransomware victim disclosure
← All victimsPyramid Analytics B.V.
Claimed by AUR0RA · listed 3 hours ago
Status timeline
- ListedSep 17, 2026
Current state: Listed for ransom
At a glance
- Group
- AUR0RA
- Status
- Listed for ransom
- Country
- Netherlands
- Sector
- Technology
- Listed on leak site
- Sep 17, 2026
- Data size
- 22 GB
About the victim
AI dossier — public-source company profilePyramid Analytics is a decision-intelligence platform company headquartered in Amsterdam that provides AI-powered business analytics, data preparation, and self-service analytics tools. The company was acquired by ServiceNow. It serves enterprises with data connectors, semantic modeling, and generative BI capabilities across multiple cloud deployments.
- Industry
- Business Intelligence & Analytics Software
- Address
- Amsterdam, Netherlands
Attack summary
Severity: critical — Confirmed exfiltration of source code, production database backups, plaintext credentials, SSL private keys enabling MITM attacks, customer data from publicly traded companies, and documented security vulnerabilities with exploits. High-value intellectual property and operational security compromise.AUR0RA claims to have exfiltrated 10+ copies of the platform source code with full Git history, wildcard SSL private keys, API credentials (Bing Maps, Mapbox, Google Sheets), database passwords, 22 GB of SQL Server production backups, customer data from publicly traded companies (Shufersal and ABB), documented security vulnerabilities with exploit methodology, and complete AI integration architecture details.
Data the group says was taken
AI dossier — extracted from the leak post- Platform source code with full Git history
- Wildcard SSL private key for *.pyramidanalytics.com
- API keys and service account credentials
- Database passwords in plaintext
- SQL Server production database backups
- User accounts and credentials
- Customer data from Shufersal and ABB
- Security vulnerability documentation with exploit methodology
- OWASP ZAP scan reports
- AI integration architecture and credentials
What the group claims
Decision-intelligence platform company headquartered in Amsterdam, acquired by ServiceNow (NYSE: NOW). Exfiltrated data includes platform source code with full Git history, wildcard SSL private key, API keys and service account credentials, database passwords in plaintext, SQL Server production database backups, customer data from publicly traded companies, documented security vulnerabilities, and complete AI integration architecture.
The leak post
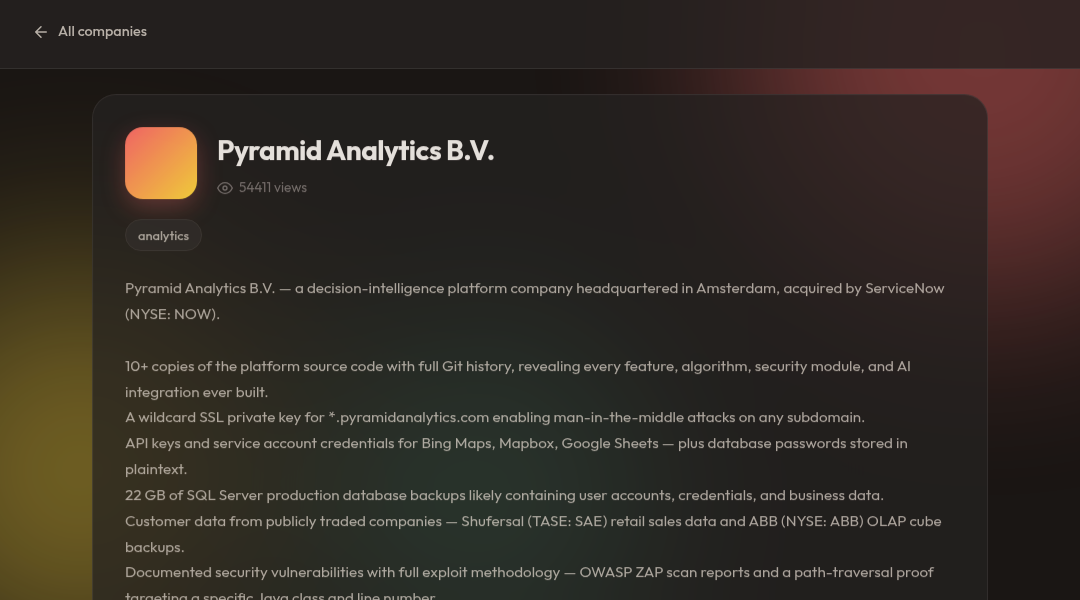
captured from the group's sitePyramid Analytics B.V. — a decision-intelligence platform company headquartered in Amsterdam, acquired by ServiceNow (NYSE: NOW). 10+ copies of the platform source code with full Git history, revealing every feature, algorithm, security module, and AI integration ever built. A wildcard SSL private key for *.pyramidanalytics.com enabling man-in-the-middle attacks on any subdomain. API keys and service account credentials for Bing Maps, Mapbox, Google Sheets — plus database passwords stored in plaintext. 22 GB of SQL Server production database backups likely containing user accounts, credentials, and business data. Customer data from publicly traded companies — Shufersal (TASE: SAE) retail sales data and ABB (NYSE: ABB) OLAP cube backups. Documented security vulnerabilities with full exploit methodology — OWASP ZAP scan reports and a path-traversal proof targeting a specific Java class and line number. The complete AI integration architecture showing connections to Google Gemini, OpenAI, Azure AI, and IBM Watsonx.
Data the group says was taken
- source code
- SSL private keys
- API keys
- service account credentials
- database passwords
- database backups
- customer data
- security vulnerability reports
- AI integration architecture
Screenshot of the leak post
Sources
Source
Indexed 3 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.