

Ransomware victim disclosure
← All victimsItaly (Government/Institution)
Claimed by IAMNOTAVILLAIN · listed 4 hours ago
Status timeline
- ListedOct 5, 2026
Current state: Listed for ransom
At a glance
- Group
- IAMNOTAVILLAIN
- Status
- Listed for ransom
- Country
- Italy
- Sector
- Government
- Listed on leak site
- Oct 5, 2026
- Data size
- 150GB
- Records
- 85000+
About the victim
AI dossier — public-source company profileItalian government institution(s) across multiple top-level departments, units, and offices. Scale and specific organizational structure not detailed in the leak post.
- Industry
- Government/Public Administration
Attack summary
Severity: critical — Claimed exfiltration of large-scale government records (150GB, 85,000+ files) affecting multiple departments, plus alleged compromise of financial services customer data (KYC, banking, crypto transactions). If verified, this represents exposure of state records and regulated financial data at scale. Extortion element (data exclusion for payment) present.IAMNOTAVILLAIN claims exfiltration of 85,000+ files (150GB) from Italian government departments for alleged failures to follow data protection laws. The group also claims to possess Revolut user data (KYC documents, addresses, phone numbers, emails, bank and crypto transaction records) allegedly sent to them by Revolut itself, and offers data exclusion for payment.
Data the group says was taken
AI dossier — extracted from the leak post- Government files and records (85,000+ files)
- Revolut KYC documents
- Personal identifiers (names, addresses, phone numbers, emails)
- Bank account information
- Fiat transaction records
- Cryptocurrency transaction records
- ID scans
What the group claims
Italy is being exposed for failing to follow proper data protection laws. Top departments, units, and offices affected.
The leak post
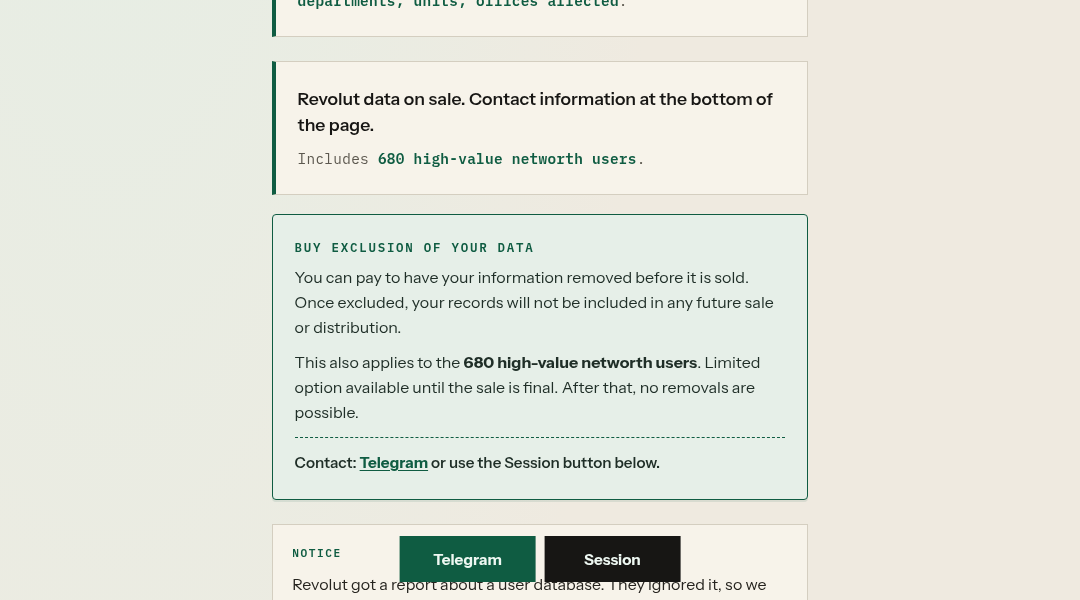
captured from the group's siteItaly is being exposed for failing to follow proper data protection laws. Includes Includes 85,000+ Files — 150GB. Top departments, units, offices affected. Revolut data on sale. Contact information at the bottom of the page. ### Buy exclusion of your data You can pay to have your information removed before it is sold. Once excluded, your records will not be included in any future sale or distribution. This also applies to the . Limited option available until the sale is final. After that, no removals are possible. Contact: or use the Session button below. Revolut got a report about a user database. They ignored it, so we are exposing them for failing to keep user information secure, and for sending data from a different jurisdiction. We have everything, including KYC documents, address, phone number, email, bank accounts, and fiat and crypto transactions. An impersonator and scammer who used to work with us took a small sample we handed him and is now claiming the breach as his. That cut is not the full set. Revolut and the other companies sent the data to us. He did not do this. We can prove it: the originals, the volume, the conversations, and the companies that sent it.…
Data the group says was taken
- files
Screenshot of the leak post
Sources
Source
Indexed 4 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.