

Ransomware victim disclosure
← All victimsBretford Manufacturing, Inc.
Claimed by AUR0RA · listed 42 minutes ago
Status timeline
- ListedSep 30, 2026
- Data leakeddate unknown
At a glance
- Group
- AUR0RA
- Status
- Data leaked
- Country
- United States
- Sector
- Manufacturing
- Listed on leak site
- Sep 30, 2026
- Records
- 200-400+ employees (current and historical) plus dependents
About the victim
AI dossier — public-source company profileBretford Manufacturing, Inc. is a privately held manufacturer of charging solutions for mobile devices, headquartered in Franklin Park, Illinois. Founded in 1948, the company employs approximately 60 people and serves education, healthcare, retail, and government sectors with annual revenue around $10 million.
- Industry
- Mobile Device Charging Solutions Manufacturing
- Address
- 11000 Seymour Avenue, Franklin Park, IL 60131
- Employees
- 60
- Founded
- 1948
Attack summary
Severity: critical — Confirmed exfiltration of highly sensitive regulated data at scale: complete SSN inventory (260–460+ individuals across 16 years), comprehensive banking and financial credentials, medical/disability/drug test records, and full network/security infrastructure details. Credential vault compromise with documented weak password culture enables cascading lateral movement.AUR0RA claims to have exfiltrated comprehensive operational, financial, and personnel data including credential vaults, AWS keys, banking account information, network architecture, and 20 years of HR and payroll records spanning 2010–2026. The group published samples demonstrating access to KeePass password files, plaintext credentials, SSNs, bank account details, and engineering designs.
Data the group says was taken
AI dossier — extracted from the leak post- KeePass password vault and master key
- AWS IAM access keys with secrets
- Plaintext local admin password
- Company password spreadsheet
- Social Security Numbers (60 current + 200–400 historical employees and dependents)
- ACA Census files
- 1099 tax forms
- Payroll records (2010–2026)
- Corporate bank account credentials
- 26+ vendor bank account credentials
- NACHA ACH batch files
- Network architecture and topology diagrams
- VPN gateway IP and infrastructure inventory
- Active Directory domain name
- Disaster recovery plan
- 20 years HR records (medical leave, disability, drug tests, garnishments, pension, 401k, insurance)
- Termination records
- SolidWorks CAD files and product designs
- CNC/laser manufacturing programs
- Manufacturing process documentation
What the group claims
Privately held manufacturer of charging solutions for mobile devices, founded in 1948 and headquartered in Franklin Park, Illinois. Serves education, healthcare, retail, and government sectors. Approximately 60 employees and ~$10M annual revenue.
The leak post
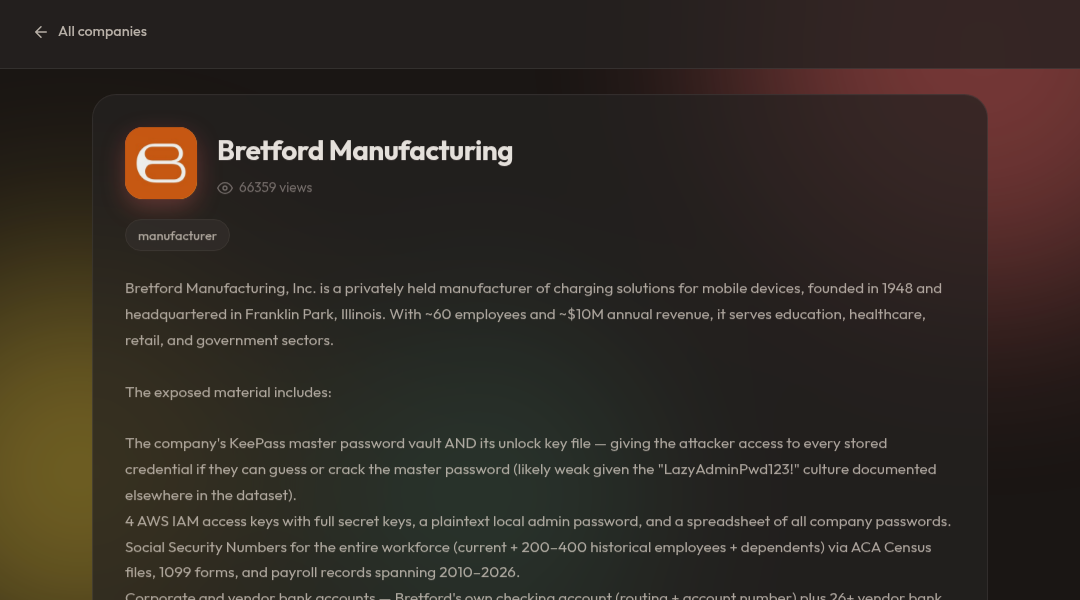
captured from the group's siteBretford Manufacturing, Inc. is a privately held manufacturer of charging solutions for mobile devices, founded in 1948 and headquartered in Franklin Park, Illinois. With ~60 employees and ~$10M annual revenue, it serves education, healthcare, retail, and government sectors. The exposed material includes: The company's KeePass master password vault AND its unlock key file — giving the attacker access to every stored credential if they can guess or crack the master password (likely weak given the "LazyAdminPwd123!" culture documented elsewhere in the dataset). 4 AWS IAM access keys with full secret keys, a plaintext local admin password, and a spreadsheet of all company passwords. Social Security Numbers for the entire workforce (current + 200–400 historical employees + dependents) via ACA Census files, 1099 forms, and payroll records spanning 2010–2026. Corporate and vendor bank accounts — Bretford's own checking account (routing + account number) plus 26+ vendor bank accounts from NACHA ACH batch files. Complete network architecture — VPN gateway IP, internal topology diagram, IP allocation tables, infrastructure inventory, disaster recovery plan, and Active Directory domain name.…
Data the group says was taken
- KeePass master password vault
- KeePass unlock key file
- AWS IAM access keys
- plaintext local admin password
- company password spreadsheet
- Social Security Numbers
- ACA Census files
- 1099 forms
- payroll records
- corporate bank account details
- vendor bank account details
- NACHA ACH batch files
- VPN gateway IP
- network topology diagrams
- IP allocation tables
- infrastructure inventory
- disaster recovery plan
- Active Directory domain information
- HR records
- medical leave records
- disability accommodation records
- drug test records
- garnishment records
- pension records
- 401(k) records
- insurance enrollment records
- termination records
- SolidWorks CAD files
- CNC/laser programs
- manufacturing process documentation
Screenshot of the leak post
Sources
Source
Indexed 42 minutes agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.