

Ransomware victim disclosure
← All victimsBuford-Thompson Company, LTD
Claimed by AUR0RA · listed 1 day ago
Status timeline
- ListedOct 1, 2026
- Data leakeddate unknown
At a glance
- Group
- AUR0RA
- Status
- Data leaked
- Country
- United States
- Sector
- Construction
- Listed on leak site
- Oct 1, 2026
- Data size
- 1.707 TB
- Records
- 350+ employees, 2000+ donor records, 36+ active projects
About the victim
AI dossier — public-source company profileBuford-Thompson Company, LTD is a Texas-based general construction contractor with over 30 years of history specializing in school construction for K-12 districts across the state. The company manages 36+ active school construction projects and maintains relationships with multiple Independent School Districts (ISDs).
- Industry
- Construction – General Contracting (K-12 School Projects)
- Address
- Texas, US
- Employees
- 30+
Attack summary
Severity: critical — Confirmed exfiltration of regulated PII at scale (350+ SSNs in plaintext), attorney-client privileged material, complete banking credentials and infrastructure, and sensitive construction/bid data for critical K-12 infrastructure projects. Multiple regulated data types present.AUR0RA claims to have exfiltrated 1.707 TB of data including 5 years of employee W-2 records with plaintext Social Security numbers for 350+ current and former employees, complete banking infrastructure and account credentials for Frost Bank, litigation discovery files containing attorney-client privileged communications, school construction project blueprints and cost structures, and incidental personal records of the Thompson family owners.
Data the group says was taken
AI dossier — extracted from the leak post- W-2 and EFW2 files (2021–2025) with plaintext SSNs for 350+ employees
- Attorney-client privileged litigation files (Stanton ISD v. BTC)
- Frost Bank account numbers, ACH routing credentials, and bank statements (2022–2026)
- 36+ active school construction project blueprints, bid estimates, and cost structures
- Subcontractor pricing and change orders
- Thompson family personal insurance, loans, property records, and tax documents
- Employee addresses and wage information
What the group claims
Texas construction general contractor with 30+ years of history building schools for K-12 districts across the state.
The leak post
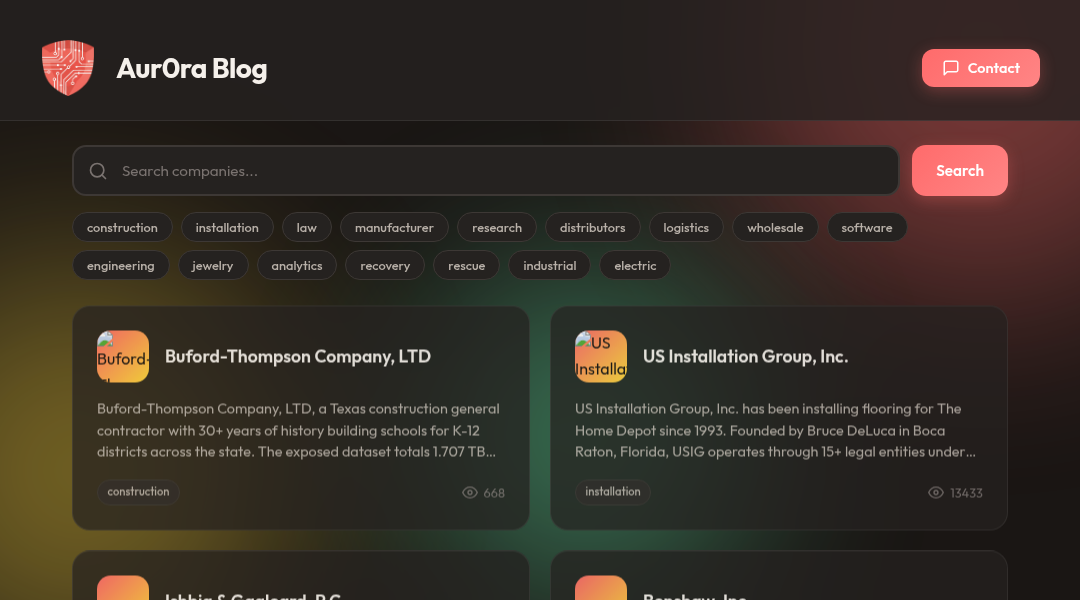
captured from the group's site[ Buford-Thompson Company, LTD, a Texas construction general contractor with 30+ years of history building schools for K-12 districts across the state. The exposed dataset totals 1.707 TB and includes: 5 years of W-2 EFW2 files (2021–2025) containing plaintext Social Security numbers, wages, and addresses for 350+ current and former employees — every SSN readable without any decryption. 9.3 GB of attorney-client privileged files from the Stanton ISD v. BTC litigation — legal strategy, discovery responses, and counsel communications. Complete Frost Bank infrastructure — four account numbers, ACH routing credentials, line-of-credit agreements (renewed April 2026), signature cards, and monthly bank statements spanning 2022–2026. 36+ active school construction projects — blueprints, bid estimates, cost structures, subcontractor pricing, and change orders for ISD projects across Texas. A competitor's dream dataset. 2,000+ donor records from Human Services Campus (Phoenix homeless-services nonprofit) with full PII: name, address, phone, email, employer, and donation amounts. QuickBooks company files (.QBW) from Along Side Ministries (Phoenix prison ministry) containing complete accountin…
Data the group says was taken
- W-2 EFW2 files
- Social Security numbers
- wages
- addresses
- attorney-client privileged files
- litigation documents
- bank account numbers
- ACH routing credentials
- line-of-credit agreements
- bank statements
- blueprints
- bid estimates
- subcontractor pricing
- change orders
- donor records
- QuickBooks files
- personal tax documents
- personal insurance
- loan documents
- property records
Screenshot of the leak post
Sources
Source
Indexed 1 day agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.