

Ransomware victim disclosure
← All victimsFREYWILLE
Claimed by AUR0RA · listed 2 hours ago
Status timeline
- ListedOct 11, 2026
- Data leakeddate unknown
At a glance
- Group
- AUR0RA
- Status
- Data leaked
- Country
- Austria
- Sector
- Luxury Goods / Retail
- Listed on leak site
- Oct 11, 2026
- Records
- 142+ employee files
About the victim
AI dossier — public-source company profileFreywille is an Austrian luxury fire-enamel jewelry house operating 70+ boutiques across Europe, the Americas, Middle East, and Asia-Pacific. The company is known for its distinctive enamel technique and product lines in 18-carat gold, plated, and textile goods.
- Industry
- Luxury Goods & Jewelry
- Employees
- 70+
Attack summary
Severity: critical — Confirmed exfiltration of regulated PII at scale (142+ employee files with SSN, passport copies, visa statements across 24 countries), banking credentials for multinational financial institutions, and trade secrets (proprietary enamel formulations). Scale and multi-jurisdictional nature of employee data elevates to critical.AUR0RA claims to have exfiltrated 14+ corporate password databases (2015–2020), 6 KeePass vaults, banking credentials for 15+ financial institutions, 142+ employee files with personal/financial data, proprietary product costing and enamel color formulations, and litigation documentation spanning multiple countries.
Data the group says was taken
AI dossier — extracted from the leak post- Corporate password databases (14+ in plaintext Excel)
- KeePass vaults (6 regional)
- Banking credentials (15+ institutions)
- MultiCash banking access
- Employee files (142+ with SSN, contracts, vaccination records)
- Passport copies and visa statements
- Salary statements (2024–2026)
- Product costing (2025 all lines)
- Enamel color formulations (SPHINX, JOYB2, Entwurf)
- Legal/litigation files (40+ lawsuits)
- 2018 webshop malware incident documentation
What the group claims
Austrian luxury fire-enamel jewelry house with 70+ boutiques across Europe, the Americas, Middle East, and Asia-Pacific. Stolen data includes corporate password databases, KeePass vaults, banking credentials for 15+ financial institutions, employee records across 24 countries, trade secrets including enamel colour recipes, legal defense files from 40+ lawsuits, and documentation of a 2018 webshop malware attack.
The leak post
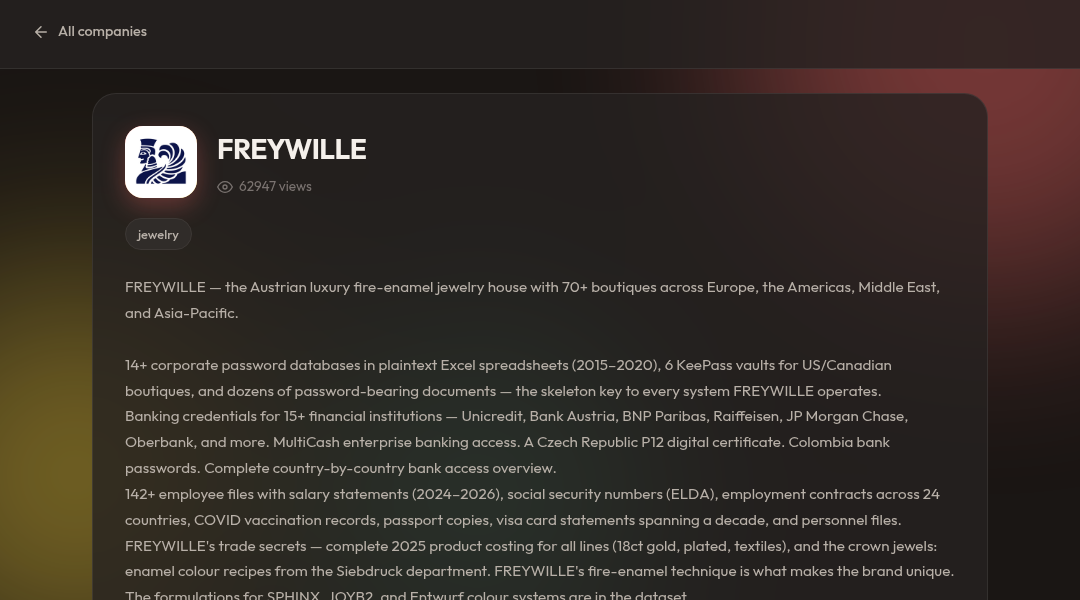
captured from the group's siteFREYWILLE — the Austrian luxury fire-enamel jewelry house with 70+ boutiques across Europe, the Americas, Middle East, and Asia-Pacific. 14+ corporate password databases in plaintext Excel spreadsheets (2015–2020), 6 KeePass vaults for US/Canadian boutiques, and dozens of password-bearing documents — the skeleton key to every system FREYWILLE operates. Banking credentials for 15+ financial institutions — Unicredit, Bank Austria, BNP Paribas, Raiffeisen, JP Morgan Chase, Oberbank, and more. MultiCash enterprise banking access. A Czech Republic P12 digital certificate. Colombia bank passwords. Complete country-by-country bank access overview. 142+ employee files with salary statements (2024–2026), social security numbers (ELDA), employment contracts across 24 countries, COVID vaccination records, passport copies, visa card statements spanning a decade, and personnel files. FREYWILLE's trade secrets — complete 2025 product costing for all lines (18ct gold, plated, textiles), and the crown jewels: enamel colour recipes from the Siebdruck department. FREYWILLE's fire-enamel technique is what makes the brand unique. The formulations for SPHINX, JOYB2, and Entwurf colour systems are in th…
Data the group says was taken
- password databases
- KeePass vaults
- banking credentials
- digital certificates
- employee files
- salary statements
- social security numbers
- employment contracts
- COVID vaccination records
- passport copies
- visa card statements
- personnel files
- product costing documents
- trade secrets
- enamel colour recipes
- legal defense files
- incident reports
- DSB filings
- customer notification drafts
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.