

Ransomware victim disclosure
← All victimsThomas Y. Pickett & Co., Inc.
Claimed by AUR0RA · listed 2 hours ago
Status timeline
- ListedOct 11, 2026
- Data leakeddate unknown
At a glance
- Group
- AUR0RA
- Status
- Data leaked
- Country
- United States
- Listed on leak site
- Oct 11, 2026
- Data size
- 127 GB (13 SQL Server database backups) + 11 GB Azure DevOps repository
- Records
- 40+ employees, 200+ client contracts
About the victim
AI dossier — public-source company profileThomas Y. Pickett & Co., Inc. is one of the oldest property tax appraisal consulting firms in the United States, founded in 1926 and headquartered in Addison/Dallas, Texas. The firm appraises mineral, industrial, and utility properties for county appraisal districts across multiple states including Texas, Wyoming, North Dakota, Mississippi, and Oklahoma, with approximately 40 employees and ~$5.3M annual revenue.
- Industry
- Property Tax Appraisal Consulting
- Address
- Addison/Dallas, Texas, United States
- Employees
- 40
- Founded
- 1926
Attack summary
Severity: critical — Confirmed exfiltration of PII at scale (40+ employees' complete identity packages including SSNs, medical records), regulated HR documentation, proprietary source code, sensitive business intelligence (client contracts with county pricing), financial records, and cryptographic materials enabling document forgery and system impersonation. The combination of identity data, medical records, credentials, and signing certificates creates severe identity theft and operational risk.The AUR0RA group claims to have exfiltrated 127 GB of SQL Server database backups (including the complete TYPortal web portal database with property owner records and credentials) and 11 GB of Azure DevOps source code repository. The group also claims to have obtained comprehensive HR records, client contracts with competitive pricing, complete financial records, and cryptographic materials including a PKCS#12 digital signing certificate.
Data the group says was taken
AI dossier — extracted from the leak post- SQL Server database backups (TYPortal web portal)
- Property owner records and user credentials
- HR records (Social Security cards, W-4s, direct deposit forms, salary schedules, medical records)
- Azure DevOps repository with proprietary COBOL source code
- 200+ client contracts with county-level pricing
- Bank statements and 10-year financial records
- Developer passwords and PKCS#12 digital signing certificate
- Payroll and accounts receivable data
What the group claims
Founded in 1926, headquartered in Addison/Dallas, Texas. One of the oldest property tax appraisal consulting firms in the US, appraising mineral, industrial, and utility properties for county appraisal districts across multiple states. ~40 employees, ~$5.3M annual revenue.
The leak post
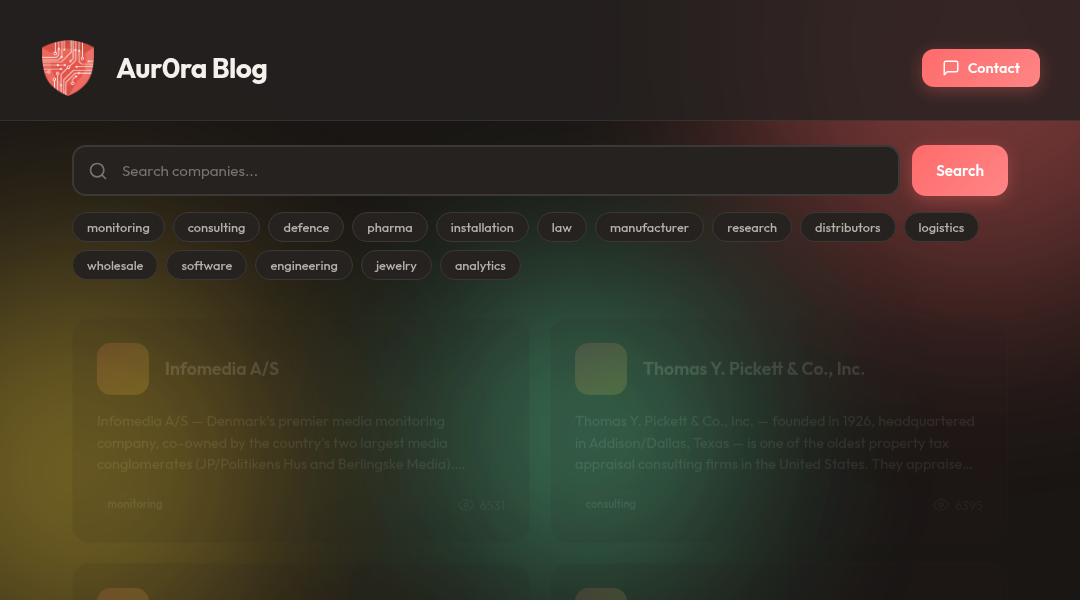
captured from the group's site[ Infomedia A/S — Denmark's premier media monitoring company, co-owned by the country's two largest media conglomerates (JP/Politikens Hus and Berlingske Media). Infomedia sits at the heart of Nordic media. It monitors newspapers, broadcasts, and digital sources for hundreds of corporate and government clients — including the EU Parliament, A.P. Møller-Mærsk, and major Nordic media groups (Schibsted, Polaris, NRK, Amedia). The exposed material spans: <redacted> <redacted> SQL Server sysadmin credentials — sa / ballmer for the Opoint CRM database at crmdb.opoint.com. An RSA private key — the TLS key for the Infomedia Export Data API service. Named salary specifications for 100+ employees across Denmark (2010–2018) and Estonia (2009–2024). 30 GB of Finance data — income statements, balance sheets, insurance policies, Danske Bank payment records, vendor contracts, tax certificates. <redacted> <redacted> ](http://u6lieui2dakbctcjea2bz4r4q32r7t36nwljovqbv7mxs6o2smgxixid.onion/blog/infomedia-as-9c5b3698)### [Thomas Y. Pickett & Co., Inc. Thomas Y. Pickett & Co., Inc. — founded in 1926, headquartered in Addison/Dallas, Texas — is one of the oldest property tax appraisal consulting firms i…
Data the group says was taken
- SQL Server database backups
- HR records
- Social Security cards
- W-4 forms
- direct deposit forms
- salary schedules
- medical records
- termination documents
- source code
- COBOL source code
- client contracts
- bank statements
- budget records
- accounts receivable
- payroll records
- PKCS#12 digital signing certificate
- user credentials
- property owner records
Screenshot of the leak post
Sources
Source
Indexed 2 hours agoThis page surfaces a public ransomware disclosure indexed by Darkfield. Original posts come from the operator's own leak site; we cross-check against ransomware.live, RansomLook and RansomWatch where applicable. Share this URL freely.
Is this your supplier? Your competitor? You?
Pro plans monitor your domain, corporate emails, and crypto wallets across every new ransomware leak-site post, breach dump and Telegram callout — alerts within 5 minutes.